About
Security leadership that speaks human.
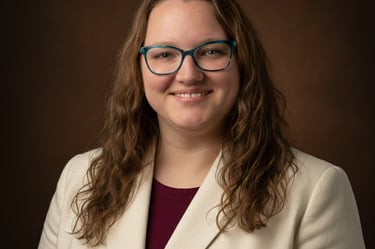
I'm Carrie Savola (SAH-vo-la), MSIA, CISSP; an IT, Information Security, and GRC professional based in the Pacific Northwest. I founded Ariadne (Air-Eee-Add-Nee) Advisory to bring real security expertise to the businesses that are usually priced out of it: solo owners, freelancers, and small teams building real things and serving real clients under real security threats. Consulting is still available for mid-size organizations that need deeper support, but small and solo businesses are the focus.
In Greek myth, Ariadne gave Theseus a single thread to navigate the Labyrinth and find his way back out. She didn't fight the Minotaur for him, she made sure he didn't get lost. That's the model for this practice. Threats, risks, and compliance mazes aren't going away, and it's not my job to slay them for you. It's my job to hand you the thread: a clear, workable path through, and a way back out the other side with your business intact.
My background spans identity and access management, governance, risk, AI governance, and compliance program design at organizations including U.S. Bank, eBay and Puget Sound Energy. I specialize in translating complex security requirements into programs that solo owners and small teams can actually use without a dedicated IT department or compliance staff to lean on.
I believe security is fundamentally a human problem. The best technology in the world won't protect you if your people don't understand the risks. My approach combines rigorous technical expertise with a deep commitment to building places, whether that's a team of one or two hundred. Where security is understood and actionable, not just mandated.
Credentials & Expertise
Masters of Science in Information Assurance
Certified Information Systems Security Professional (CISSP)
Governance, Risk & Compliance - 15+ Years
Identity & Access Management architecture and design
Responsible AI Governance and Policy Frameworks

Diagnostic work. Opinionated findings. Concrete next steps.
Every engagement starts with what is actually happening in your environment — not a framework checklist. The deliverable is a ranked set of risks: what is one incident away from breaking the business, and what to fix first.
Compliance is finished when the next questionnaire lands and you answer it without panic — not when you sign off on a report.
HIPAA · SOC 2 · NIST CSF · Cyber Insurance
10 – 200 person companies across North America
One scoped engagement. No retainer required to start.
Each framework treated as a live operational requirement — not a one-time audit artifact.
Founders, ops leaders, and finance teams who own security by default — not by choice.
The Security Health Check is a fixed-fee first step — findings in hand before any longer commitment.